How to Spot a Phishing Email Before It Costs You
Phishing emails have gotten dramatically harder to spot over the past few years. The obvious red flags — broken English, absurd requests, sketchy links to unfamiliar domains — have largely given way to convincing, well-written messages that mimic real vendors, colleagues, and even your own company’s internal communications. Recognizing them now requires a sharper, more deliberate process than the old “check for typos” advice ever provided.
Step 1: Slow Down Before You Act on Urgency
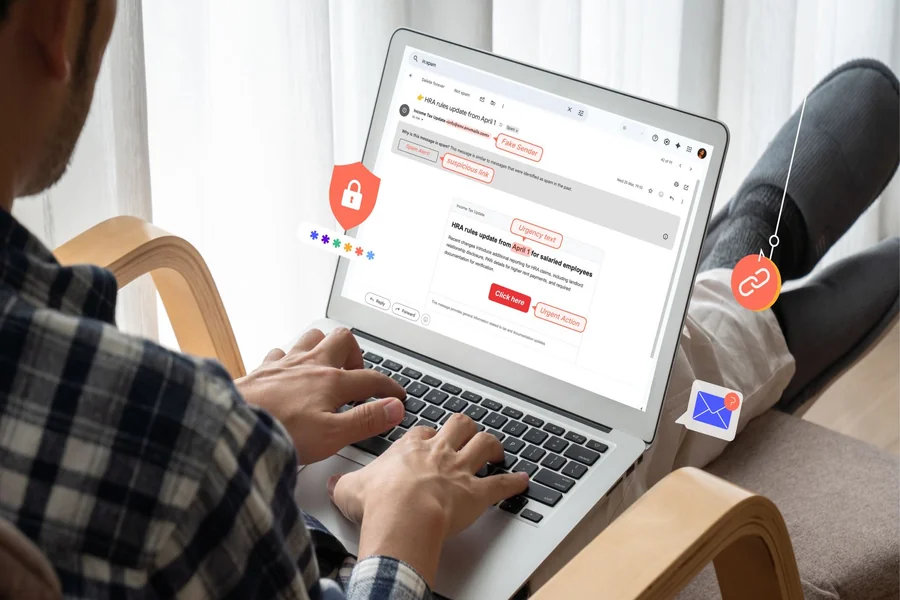
The single most consistent trait across almost every phishing attempt is manufactured urgency — an invoice that needs immediate payment, an account that will be suspended within hours, a request from “the CEO” that needs handling right now, before there’s time to think it through. Legitimate requests can usually tolerate a two-minute pause to verify. If a message is specifically designed to prevent that pause, treat the urgency itself as the red flag.
Step 2: Check the Actual Sender Address, Not Just the Display Name
Attackers routinely spoof a display name that looks exactly like someone you know while the underlying email address is completely different. Click or hover on the sender’s name to reveal the full address, and look closely — attackers frequently use addresses that are one character off from a legitimate domain, something easy to miss at a glance but obvious once you’re actually looking for it.
Step 3: Hover Before You Click, Every Time
Before clicking any link in an email, hover over it to see where it actually leads. A link that displays as your bank’s website but points to a completely unrelated domain is one of the clearest and most reliable signals available. This habit takes about two seconds and catches an enormous share of phishing attempts on its own.
Step 4: Be Especially Skeptical of Attachments You Weren’t Expecting
An unexpected invoice, shipping notification, or “signed document” you weren’t anticipating deserves extra scrutiny, particularly if it arrives with pressure to open it quickly. When in doubt, verify through a separate channel — a phone call or a message through a platform you know is legitimate — rather than replying to the email itself, since a compromised account will simply confirm whatever the attacker wants you to believe.
Step 5: Watch for Requests That Bypass Normal Process
If a request asks you to skip a usual step — approving a wire transfer without the normal second signature, changing payroll deposit information through email instead of the usual HR system, sharing credentials “just this once” for an urgent fix — treat the process bypass itself as suspicious, regardless of how convincing the surrounding message sounds.
Step 6: Verify Through a Second Channel for Anything Involving Money or Credentials
Any request involving a financial transaction, a password, or sensitive data deserves verification through a channel other than the one the request arrived on. If an email claims to be from your CFO asking for an urgent wire transfer, a quick phone call or a message on a separate platform confirms it in under a minute and has stopped countless real incidents before they became expensive ones.
Step 7: Report It, Even If You’re Not Certain
Most organizations would rather receive ten false alarms than miss one real phishing attempt. Reporting a suspicious email — to your IT team, a security tool, or however your organization has set this up — takes a moment and helps flag the same message before it reaches a colleague who might not catch it.
Step 8: Build the Habit Organization-Wide, Not Just for Yourself
Individual vigilance helps, but phishing resistance is really an organizational habit. Regular training, simulated phishing tests, and a genuinely blame-free reporting culture consistently outperform relying on any single employee’s sharp eye. A managed IT partner running periodic phishing simulations can be a useful way to keep this skill sharp across a whole team without requiring constant internal effort to maintain it.
Phishing will keep evolving, and no checklist stays perfect forever. But slowing down, verifying independently, and treating urgency itself with suspicion will catch the overwhelming majority of what lands in your inbox.